 Cloud & Business Apps
 Cybersecurity
 Data & AI
 IoT & Connectivity
 Industry
 Health
 Banking and Finance
 Public Sector
 Retail
 Tourism and Leisure
 Transport & Logistics
 Energy & Utilities
 Smart Cities

Identity Fabric: what it is and how it helps protect and enable the business
Managing the identities of people, machines and AI agents within a single framework links every access decision to risk and business needs. Telefónica Identity Fabric is our integrated identity management model and the focus of this conversation with David Prieto, Head of Identity & Cryptography, and Patricia Palacín, Head of Protect & Identity Sales Specialists.
______
For years, companies have been adding different solutions to manage identities and access. What are the limitations of managing identity this way today?
Companies have gradually added tools to meet specific needs: workforce access, protecting critical systems, supplier access or customer access. Each one solved a particular problem, but when they operate in isolation, processes become disconnected and no one has the full picture.
In practice, you see it straight away. Someone moves to another department and keeps the permissions from their previous role. A supplier's contract ends and their account remains active for months. An audit comes around and exports from four different tools have to be cross-checked by hand just to find out who has access to what. These are situations we see in almost every organisation we work with, in both the public and private sectors.
The value comes when solutions stop operating in isolation and are connected under a common governance framework.
At the same time, the concept of identity has expanded far beyond employees. What should an enterprise identity strategy cover today?
Any person, machine or AI agent that accesses information or acts on systems: employees, citizens, customers, suppliers and partners, but also applications, service accounts, devices, workloads and agents, across on-premises, Cloud and hybrid environments.
Non-human identities are already in the majority. The latest industry studies put the ratio at more than 100 machine identities for every person in many companies, and a growing proportion of these are AI agents. Yet most identity programmes are still designed only for people.
The governance framework can be common, but each type of identity needs different controls. A citizen accessing a public service needs a simple experience that respects their privacy. A service account needs a named individual owner and credentials that are regularly rotated. An AI agent needs limits that reflect its degree of autonomy.
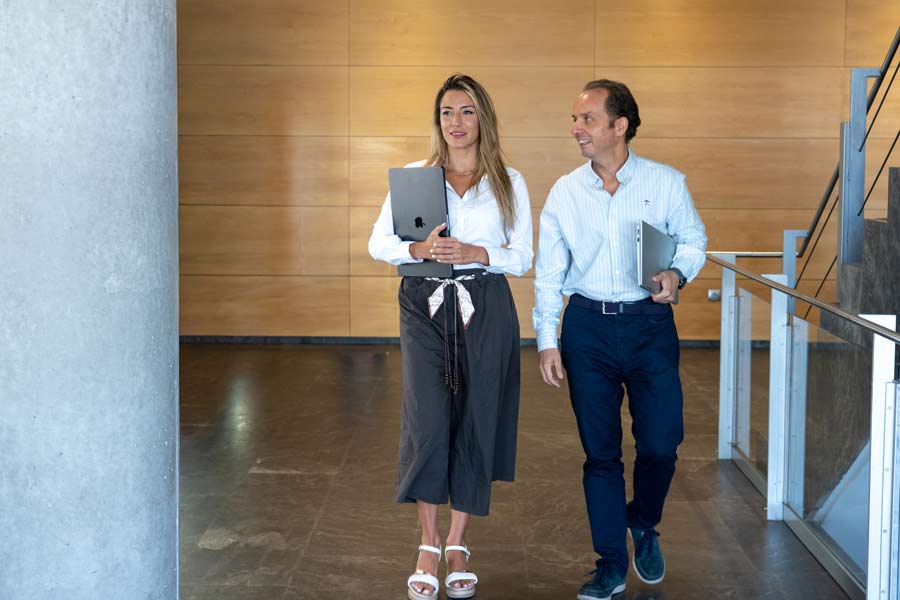
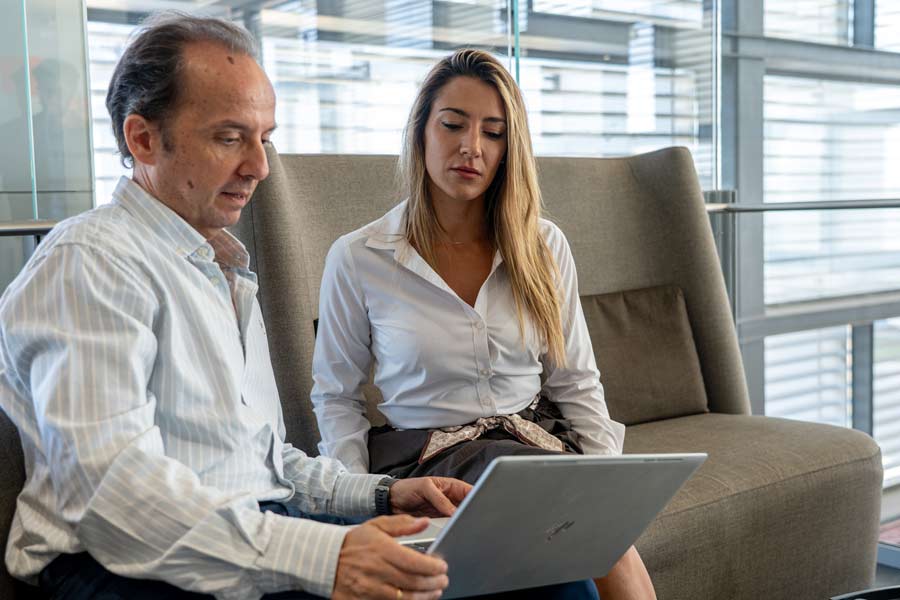 David Prieto (left), Head of Identity & Cryptography, and Patricia Palacín, Head of Protect & Identity Sales Specialists.
People, machines and AI agents need a common governance framework, with controls tailored to their nature and level of risk.
Given this complexity, how does the way companies manage identity need to evolve?
In hybrid and distributed environments, it is no longer enough to know where someone is connecting from. You need to know who or what is acting, on whose behalf, for what purpose, on which resource, with what privileges and at what level of risk.
To do that, identity governance, access management, privileges and operations need to work as a system of systems: sharing information and applying the same policies. A simple example: when Human Resources records that someone has left the organisation, the directory should disable the account, the privileged access management tool should revoke the credentials and the governance platform should record the change, without anyone having to open three separate tickets.
Identity works as a cross-cutting capability that connects tools, processes and decisions.
This is where Telefónica Identity Fabric comes in. What exactly do we mean by this model?
Telefónica Identity Fabric is our architectural, operational and governance approach to making identity the common fabric underpinning all of a company's digital relationships. It integrates capabilities, processes, data and policies to provide a single view of identities and their access.
It is not a product, nor does it require customers to replace what they already have. It is a multivendor reference architecture. If a company already manages its workforce effectively through its corporate directory, we build on that and connect identity governance, privileged access, or citizen and customer identity capabilities to it. We put this into practice through a modular catalogue of services for assessment, design, implementation and operation, tailored to each company's level of maturity.
Identity Fabric connects architecture, governance and operations so that identity decisions can be put into practice day to day.
What changes for a company when identity is managed in this integrated way?
First, the identity lifecycle. When someone joins, changes role or leaves, this automatically triggers the granting, adjustment or removal of access. A new starter has what they need from day one, and someone who leaves loses access that same day, not weeks later.
Second, visibility: who is responsible for each identity, what permissions it has and what it does with them. Access reviews stop being a spreadsheet exercise and are carried out using common criteria and with traceability.
And third, experience and agility. Fewer passwords and fewer repeated requests for employees and citizens. And a reusable foundation: when a new application or a new partner is introduced, it connects to what is already there instead of creating another isolated integration that eventually becomes technical debt.
Integrating identity speeds up access changes, improves visibility and avoids creating more isolated integrations.
One of the principles of Identity Fabric is to connect identity with the company's needs and policies. What does that relationship look like in practice, and what role does regulatory compliance play?
It is about turning business needs into concrete rules. A supplier working on a project should have access for a defined purpose, an internal owner and an expiry date, so that when the project ends, the access is removed automatically. If an operation requires segregation of duties, for example, so that the person who sets up a supplier cannot also approve its payments, the system prevents this from the outset instead of discovering it during an audit.
Regulation helps define which controls and evidence are required. Depending on the sector, ENS, NIS2 or DORA set requirements around security, risk management and access control. eIDAS 2.0 also introduces a very practical development: Member States must make the European Digital Identity Wallet available to citizens before the end of 2026, and from 2027 many private-sector organisations will have to accept it. Public administrations and companies providing digital services should already be preparing their citizen and customer identity platforms to integrate it.
Compliance is demonstrated in day-to-day operations, with evidence of how access is granted, used, reviewed and removed.
Security is one of the fundamental dimensions of Identity Fabric. How does this model help organisations move towards Zero Trust and continuously manage identity-related risk?
Zero Trust combines three principles: verify explicitly, grant only the necessary privileges and assume that a legitimate identity may have been compromised. In practice, access depends on the resource being requested, the sensitivity of the data, the device and risk signals.
And granting access is not the end of the decision. If a user signs in from their usual device and, an hour later, their account attempts to download data in bulk from another location, the system needs to react: require re-verification, limit privileges, terminate the session or block the action. This is what the market calls identity threat detection and response (ITDR), and in Identity Fabric it is part of the model by design, not something added afterwards.
Trust is assessed continuously: access can be subject to stronger controls, restricted or revoked when the context or risk changes.
The emergence of AI agents capable of making decisions and taking actions introduces a new scenario. How can a model such as Identity Fabric help govern these new identities?
The first thing is to know what each agent is: its identity, why it exists, who is accountable for it and whether it is acting on behalf of a person or the company. From there, its limits can be defined: what data it can access, which tools it can use and what actions it can take without supervision.
For example, an agent that handles incidents may be able to access the case history and prepare a solution, but if that solution involves changing permissions or authorising a payment, it needs human approval before carrying it out. Its credentials must be its own, temporary and limited to the task, never an administrator's credentials.
Traceability is essential. Every relevant action is linked to the agent, the tools it has used and the authorisations it has received, and there is a mechanism to stop it if its behaviour falls outside what is expected. All of this needs to be coordinated with the security of the applications, models and data it uses.
The greater an AI agent's autonomy, the greater the need for its own identity, clear limits on what it can do, oversight and traceability.
What value does this approach provide beyond Cybersecurity?
Integrated identity management improves the experience of employees, customers and partners: it makes it easier for them to access the services they need, speeds up onboarding and avoids repeated requests. When processes are well designed, automation reduces the administrative burden and helps maintain that agility as scale increases.
A common foundation makes it easier to integrate new applications, collaborate with third parties and develop digital services. It also helps contain the complexity and technical debt created by isolated integrations, provided the model is implemented progressively and maintained as part of day-to-day operations. The company can reuse identity and trust components, processes and integrations as it adds new services and digital relationships.
A common identity foundation makes it possible to reuse components, processes and integrations when adding new applications, services and partners.
How can a company start moving towards Identity Fabric?
With an honest assessment: what identities exist, who is responsible for them, how access is managed and where the gaps are. It needs to cover the technology, the processes and how people actually work day to day. It is very common to find workforce identity management well under control while, at the same time, technical accounts have no owner or third-party access is never reviewed.
Based on that assessment, we define a target architecture and phased roadmap with the customer, with business, security, technology and compliance all around the same table. The first steps usually focus on measures that deliver impact quickly: removing obsolete accounts and access, assigning an owner to every technical account and eliminating permanent administrative privileges. Coverage and integration can then be expanded.
And from the outset, there need to be metrics: how long it takes to remove access after someone leaves, what percentage of identities have an assigned owner, how many privileged accounts are still permanent and how many AI agents have defined permissions and operating conditions. These metrics allow us to demonstrate progress and readjust priorities.
Identity Fabric does not require everything to be transformed at once: it starts with an assessment, prioritises the highest-risk gaps and moves forward gradually and measurably.